WD 361: Brazil, JetBlue Bankruptcy, Mexican Airlines Merger
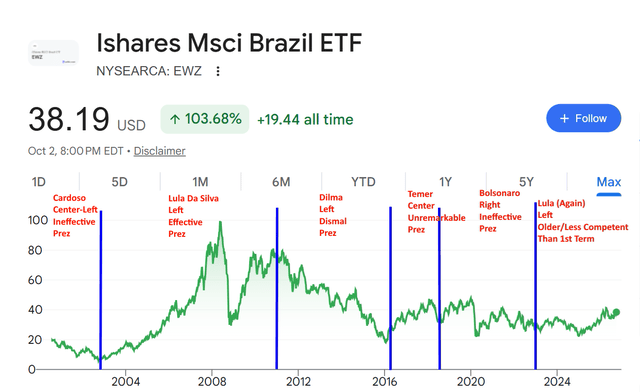
Brazil’s Lula victory leaves Nu and Inter’s thesis intact, while JetBlue heads toward bankruptcy and Mexican airlines pursue a merger.
Brazil’s Lula victory leaves Nu and Inter’s thesis intact, while JetBlue heads toward bankruptcy and Mexican airlines pursue a merger.
$GME up 50% since this post as insiders scoop up shares hand over fist https://t.co/uKFkMe6jep https://t.co/peHc0ImMzs
@RAMCOCAPITAL That is exactly where I landed! I can see how this would appeal to Buffett even if Greg couldn't get his head around it. Although like the $SNOW IPO, maybe it was someone else who made the decision.
@davidco36358214 I think the problem is the strategy is not working. Revenue, at best, can be described as choppy since 2022. The only thing $WRAP has done consistently is grow share count.
@upand_right A lot of $WOLF calls. I mean they have a unique asset that they spent $7b on, you would think eventually they get the volumes to make it viable.
Bad home in a troubled neighborhood? $DFH @BearCaveEmail https://t.co/ia5jNdAZ79 https://t.co/3vE2Slewdx
A really good $CCLD pitch that I think is very conservative with their PT. Street 12-month analyst PT is $7.33 versus circa $1.8 stock today. LINC.CareCloud.pdf

Getty Images' 2026 Chapter 11 filing is challenged as a prepack after warrant litigation, a failed Shutterstock merger and AI pressure.
Klaviyo's customer-data platform and new AI Composer product underpin a bullish growth case, with Salesforce's Braze acquisition cited as a…
 Fountainhead 2 clicks
Signet Jewelers cut its share count from 87 million to 38 million since 2012 as short interest reaches 15%, amid a hated diamond market.
Tower Semiconductor’s low-loss photonics chips halve lasers in 1.6T optical modules, supporting a $680 million annualized photonics run…
Super Micro’s 2026 xAI rack orders, GB300 price increases and B300 mix frame its gross-margin outlook.
Six Value Line small caps including Blackbaud, Marqeta, Ranger Energy and Definitive Healthcare trade on net cash, buybacks, low multiples…
Ares Capital’s 10%+ yield is supported by a $30.5 billion portfolio with over 70% floating-rate debt, though dividend coverage remains…
 Jonathan Weber 5 clicks
Petrobras’s Morpho-1 well revived hopes that Brazil’s Equatorial Margin can become a major new oil frontier after hydrocarbons were…
Applied Materials targets AI-driven demand for advanced logic, DRAM and packaging, supported by services revenue and operating leverage…
 Dhierin Bechai 2 clicks
CoreWeave’s rising debt yields and fading confidence in AI data-center economics frame a weekly review of Meta, Tesla, SpaceX, Netflix,…
 JBFCY · long
Jollibee Foods trades at PHP 144, about 56% below its January 2019 high, framing a long thesis on the Philippine restaurant operator.
CoreWeave's financial statements point to a business model familiar to the authors after a closer review of the AI infrastructure company.
DigitalOcean is pivoting toward affordable AI infrastructure and inference workloads, targeting share from AWS and Google Cloud amid…
 Star Investments 9 clicks
Bloom Energy’s Q3 FY26 revenue rose 138% to $1.24 billion as datacenter power orders lifted operating margin to 18%; capex drove $181…
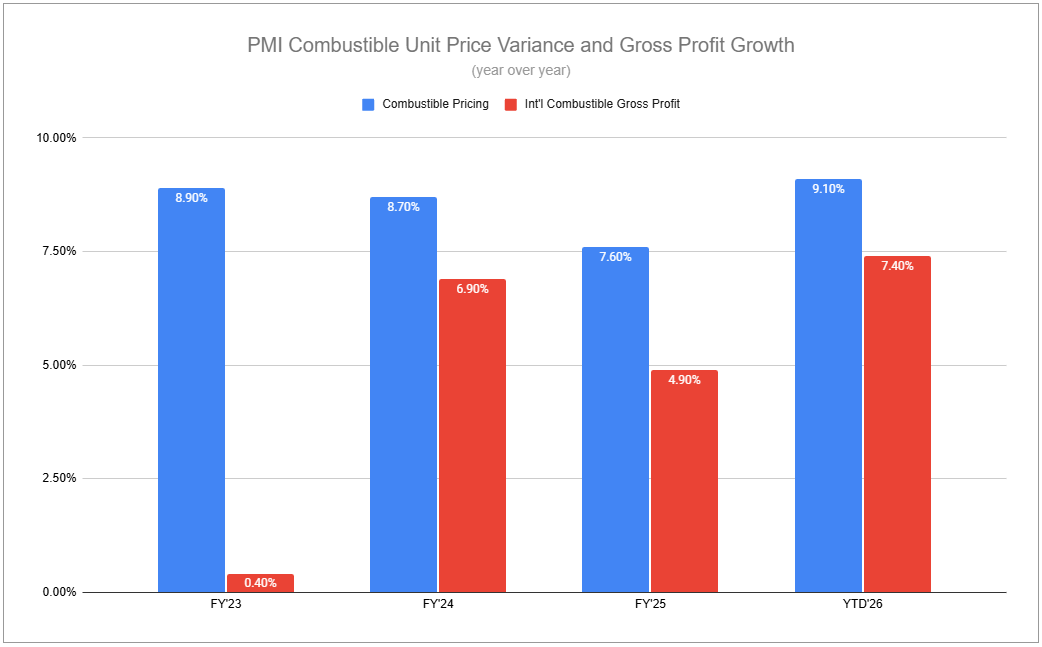
Philip Morris reported Q3 growth across heated tobacco, combustibles and e-vapor in Europe while gaining U.S. nicotine-pouch share.
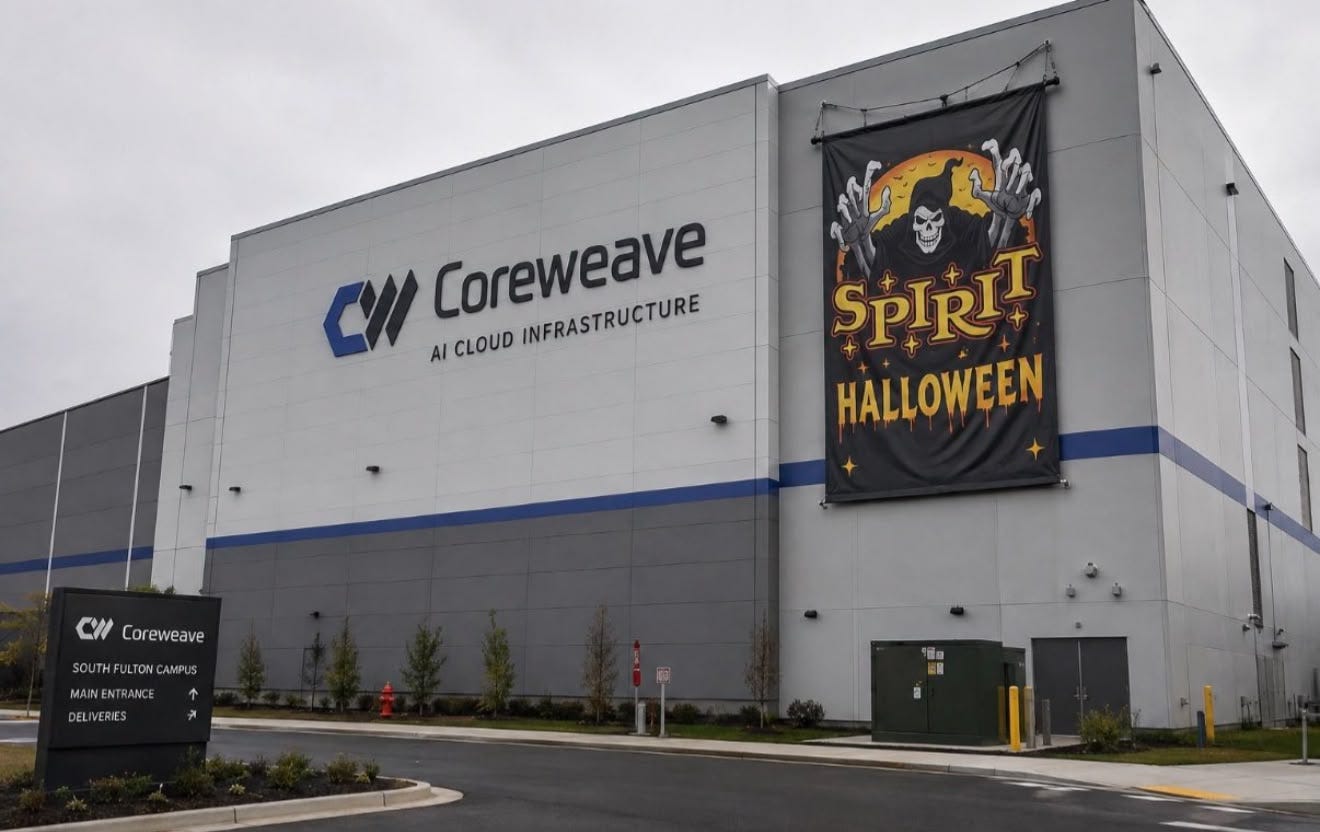
CoreWeave’s $35 billion to $39 billion 2026 spending plan relies on debt as unsecured yields reach 15%, making its GPU cloud expansion a…
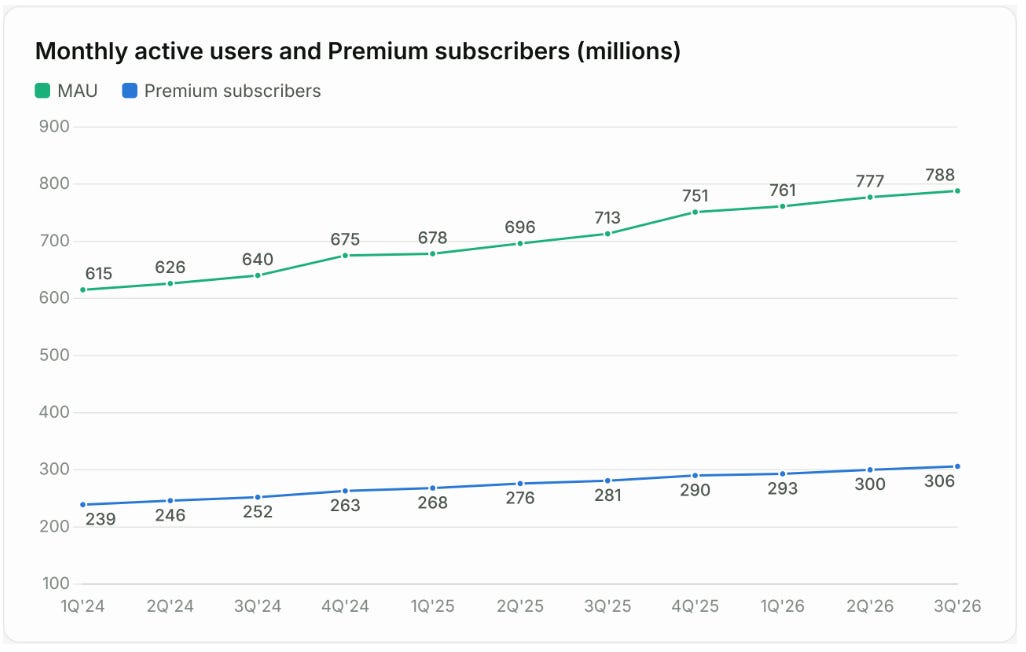
Spotify's third-quarter results met or exceeded guidance, with 306 million Premium subscribers and €672 million operating income, while…
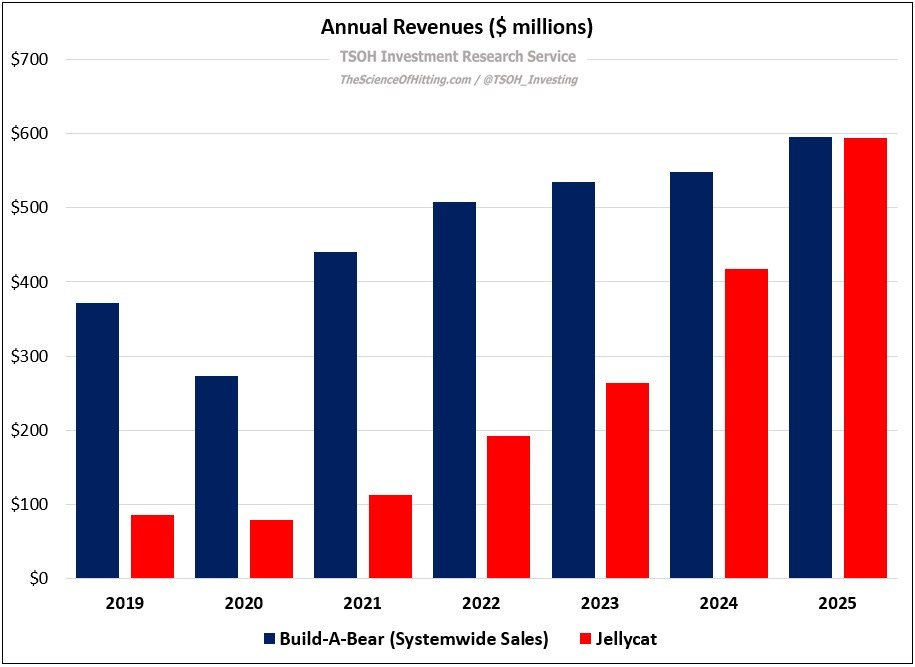
TSOH Weekly Roundup covers Ally’s improving credit and capital returns, Pepsi’s weak beverage brands, and Match Group’s plan to revive…
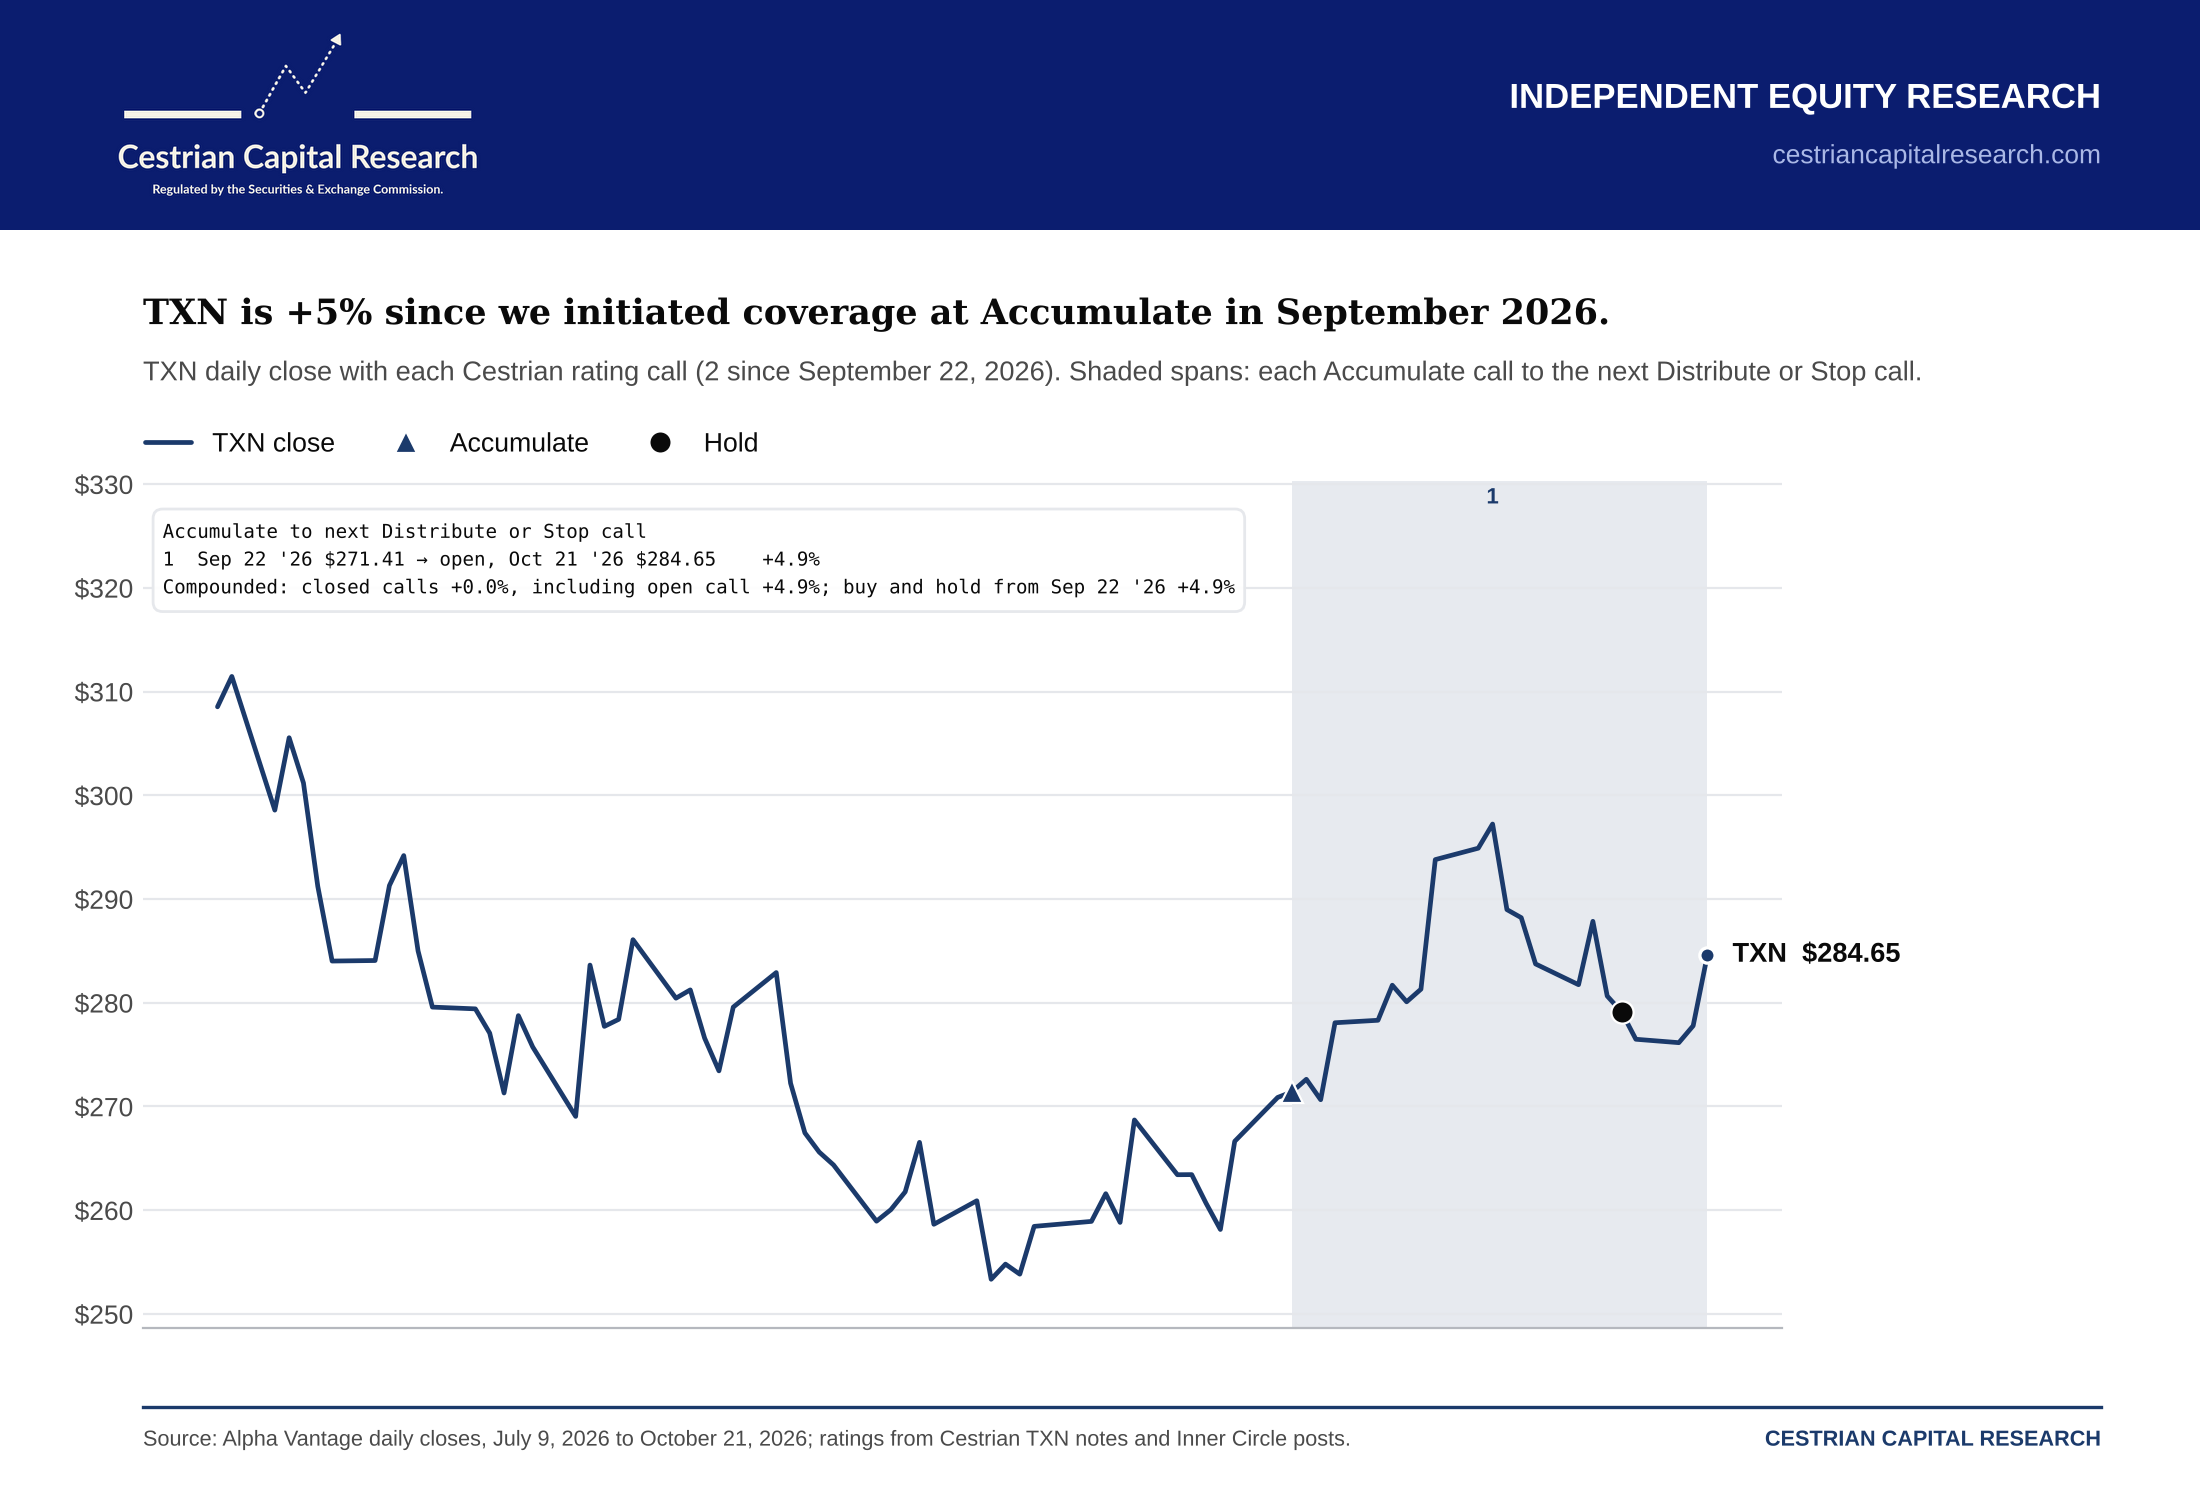
Texas Instruments reported Q3 revenue of $6.06 billion, up 28%, with 47% operating margin and Q4 guidance above seasonal norms; Cestrian…
Tempus AI targets $1.6 billion of 2026 revenue through AI diagnostics, data licensing and cancer-testing partnerships, with Personalis…
Every publication on this site, hand-picked.
 Albert Anthony
 Andres Veurink
 Bay Area Ideas
 Blake Winiecki
 Capital Connoisseur
 Dane Bowler
 David Zanoni
 Deep Value Investing Dhierin Bechai
 Dilantha De Silva
 Dustin Quasney
 Elliott Gue
 Equity Eagle
 Eudaemon Research
 Fernanda Galvez Jalil Fountainhead
 Geneva Investor
 Given Mahlangu
 Henrik Alex
 High Alpha Professor
 Ignacio Planas Gonzalez
 Investor Overview
 IWA Research
 Jaden Mealy
 JR Research
 Julia Ostian
 Khaveen Investments
 Kurt Christensen
 LL Insights
 Long Player
 Marc Gerstein
 Melissa Tucker
 Mike Zaccardi, CFA, CMT
 Miletus Research
 Myriam Alvarez
 Petri Dish Reports
 Philip Wang
 Prakhar Agarwal, CFA
 PropNotes
 PV Research
 Quantryon Capital
 Robert J. Lake
 Ron Ferrie
 Ryan Canady
 Sam Mancini
 Sharon McArd
 SiliconBytes Insights
 Simple Investment Ideas
 Sorrento Research
 Stephen Ayers
 Steven Fiorillo
 The Alpha Analyst
 The Asian Investor
 The Bullionaire
 The Curious Analyst
 The J Thesis
 The Supercycle Investor
 The Undercovered Dozen
 Tim Travis
 Value Capital Research
 Vishal Jadaun
 Zoltan Ban
Every account on this site, hand-picked.
 ⚽️📡
 💥PETITION💥
 A Capital
 absreturnchaser
 Adam D. Wyden
 Alpha Vulture
 AltayCap
 Asif Suria
 Bank Reg Blog
 Barbarian Capital
 BDC
 Bill Ackman
 Brian McGough
 Broken Moats
 BuccoCapital Bloke
 Calvin Blissett
 catechwilliams
 Charles Frischer
 Chris Camillo
 Clark Square Capital
 Cluseau Investments
 Colin King
 Connor Haley
 Conor Maguire | Value Situations
 Convequity
 Dalius - Special Sits
 David Orr
 Deep Sail Capital
 Derek Pilecki
 Devin LaSarre
 DOMO Capital Management, LLC
 Edwin Dorsey
 Evan Tindell
 Fajasy
 Farmer
 Fierce_beast
 Fred Liu
 Gavin Baker
 George Noble
 Hunterbrook
 Ian Bezek
 Idea Brunch
 JabroniCoin.USD
 John_Hempton
 junkbondinvestor
 kab60
 KEDM.com
 Kevin Mak
 Kuppy
 Laughing Water Capital
 Lee Roach
 Little Owl Research
 Maius
 Maj Soueidan
 marginofdanger
 mavix
 Mike
 Mikro Kap David
 Mr Neutral Man aka "Howard Marks of REITs”
 Multiples Capital
 Myles
 Nat Stewart
 Negligible Capital
 Odd Diligence
 Odd Lot Arbitrageur
 PAA Research
 Paradis
 Pernas Research
 Porter Collins
 Prepared Remarks
 Psyop Capital
 Raging Capital Ventures
 Red Dog Capital RiverRoadPartners
 Rohan Pavuluri
 Rusholme Capital
 Sahil Khetpal
 Serenity
 SG
 Sheel Mohnot
 SouthernValue
 Steve Eisman
 The Friendly Bear
 Tim Eriksen
 Timyan Bank Alert
 Todd Wenning
 ToffCap
 Trevor Scott
 Undiscovered Compounders
 Voss Capital
 Yaron Naymark
Ordered by how often our editor reaches for them.